SharePoint has now become a root-level platform for Intranet collaboration, document management, content management, and workflow automation in modern organizations for countless businesses worldwide. Securing this vital platform has never been more crucial.
With advanced security features, SharePoint ensures that sensitive organizational data remains protected against unauthorized access.
A properly secured SharePoint environment ensures regulatory compliance, enhances productivity through appropriate access controls, and safeguards your organisation’s most valuable data.
Understanding SharePoint Security Layers
When it comes to protecting your organization’s SharePoint environment, security works in three connected layers. Think of these layers as a complete security system where each part plays a vital role in keeping your data safe.
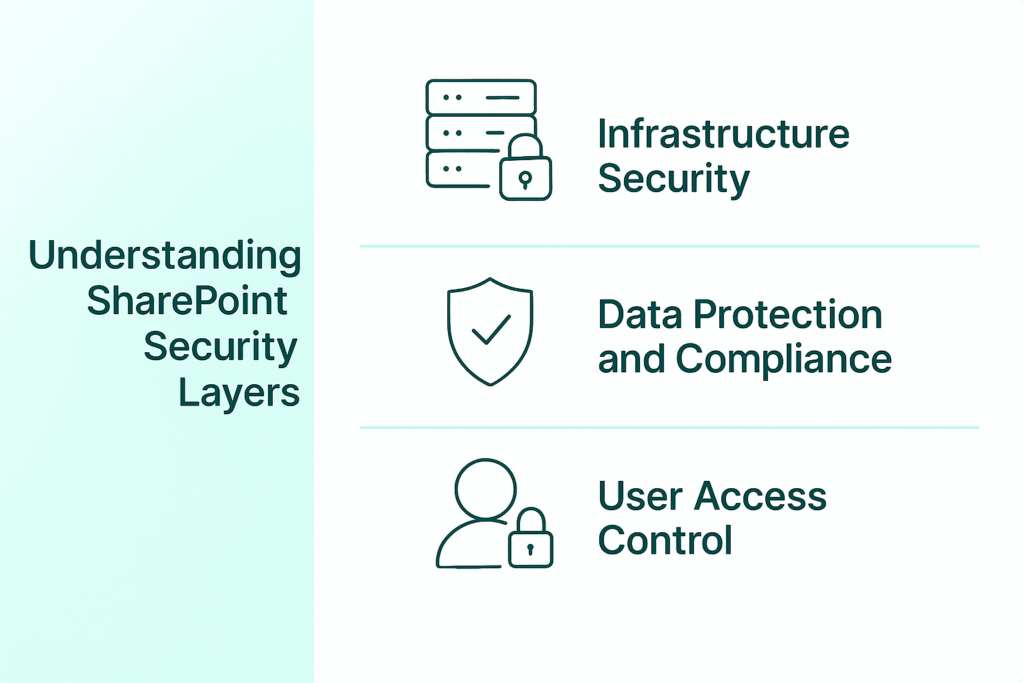
Infrastructure Security
This is the foundation of SharePoint security – the physical and technical protections that Microsoft has built into the system:
- Physical security at Microsoft’s data centers includes security guards, video surveillance, and controlled access to protect the actual servers where your data lives.
- Network protection uses advanced firewalls and monitoring systems to block malicious traffic and prevent attacks like DDoS (where hackers try to overwhelm your systems).
- Server security involves regular security testing, keeping systems updated with patches, and hardened configurations that remove unnecessary features that could be exploited.
- Encryption in transit ensures that when data moves between locations, it’s encrypted using protocols like TLS 1.2 so it can’t be intercepted.
- Customer isolation keeps different companies’ data separate from each other in Microsoft’s cloud environment
Microsoft handles most of these infrastructure concerns automatically in SharePoint Online, using industry-standard encryption like AES-256 for stored data and secure connections when data is being transferred.
Data Protection and Compliance
This layer focuses on protecting the actual information in your SharePoint environment and meeting legal requirements:
- Data Loss Prevention (DLP) automatically finds and protects sensitive information like credit card numbers or personal data by scanning content and enforcing rules you create.
- Information Rights Management adds protection that stays with documents even after they’re downloaded, preventing unauthorized sharing.
- Retention policies let you automatically keep important records for required periods and safely delete data when it’s no longer needed.
- eDiscovery tools help you find specific information when needed for legal purposes.
- Compliance features help meet regulatory requirements like GDPR (European privacy law), HIPAA (healthcare privacy), and other industry standards
Microsoft regularly updates these tools to handle new regulations, with recent improvements in 2025 including better AI-based data classification and controls for data that crosses international borders.
User Access Control
The final layer manages who can access what within your SharePoint environment:
- Authentication systems verify users’ identities, preferably using multi-factor authentication for extra security
- Permission levels create a hierarchy of access:
- Site collection administrators (highest level access)
- Site owners (can manage specific sites)
- Contributors (can add and edit content)
- Viewers (can only read content)
- Administrator protections provide extra security for accounts with high-level privileges.
- External sharing settings control how and when content can be shared with people outside your organization.
- Conditional access makes security decisions based on factors like location, device, and risk level
Best practice is to follow “role-based access control” (RBAC), which means giving people only the access they need to do their jobs nothing more. For SharePoint Online users, Microsoft provides additional tools like Privileged Access Management to further control and monitor administrative access.
By implementing security across all three layers, organizations create a “defense in depth” approach where multiple security measures work together to protect information while still allowing people to collaborate effectively.
Top 10 SharePoint Security Best Practices for 2025
SharePoint is powerful—but with great collaboration comes great responsibility. Staying ahead of threats in 2025 means going beyond default settings. You need proactive, layered security with regular reviews, automated threat detection, role-specific controls, and employee vigilance.
Below are 10 proven best practices to protect your SharePoint environment:
1. Enforce Multi-Factor Authentication (MFA)
Credential theft remains one of the most common attack vectors. MFA adds a crucial barrier that significantly reduces the chances of unauthorized access, even if a user’s password is compromised.
Why it matters: MFA blocks 99.9% of identity-related attacks (Microsoft).
Steps to implement:
- Go to Microsoft 365 Admin Center > Users > Active Users
- Click on “Multi-factor authentication”
- Enable MFA for every account, especially global admins
Best Practice: Make MFA mandatory for everyone—internal staff, external collaborators, and admins No exceptions.
2. Conduct Permission Audits—Not Once, But Regularly
Access controls often become outdated due to team changes, project closures, or employee turnover. Routine audits help maintain least-privilege access and reduce unnecessary exposure.
Audit to identify:
- Orphaned accounts (e.g., employees who have left)
- Users with excessive or irrelevant access
- External users who no longer need access
Tools to help:
- SharePoint’s native Site Permissions page
- Third-party tools: ShareGate, AvePoint, SysKit
Frequency:
- Quarterly comprehensive audits
- Monthly spot-checks for sensitive or high-risk sites
Tip: Keep a record of audits for compliance and governance.
3. Deploy Microsoft Defender for Office 365
Modern threats go beyond viruses. Defender for Office 365 protects your environment with AI-powered detection, real-time scanning, and deep threat analytics integrated with Microsoft 365.
What it includes:
- Safe Attachments: Scans files for malware before delivery
- Safe Links: Evaluates link safety at click time
- Anti-phishing: Blocks spoofing and impersonation attacks
- Threat Explorer: Provides detailed threat investigation tools
Why it works: It runs in the background without affecting performance, offering comprehensive protection across SharePoint, Teams, and OneDrive.
4. Set Up Data Loss Prevention (DLP) Policies
DLP safeguards your business from accidental or malicious data leaks by enforcing rules on how sensitive information can be shared inside and outside the organization.
Steps to implement DLP:
- Identify sensitive data categories: HR data, legal docs, IP, etc.
- Create custom information types as needed
- Define rules to alert, block, or encrypt based on severity
- Test policies to reduce false positives before full deployment
Pro Tip: Start small with warnings. Then move to blocking once you confirm accuracy.
5. Use Conditional Access for Context-Aware Controls
Context-based access ensures users connect to SharePoint only under safe, predefined conditions. It tailors access based on identity, device health, risk, or location.
What to consider:
- User role: Executives vs general staff
- Device state: Is it compliant and secure?
- Location: Trusted vs untrusted IPs or geographies
- Sign-in behavior: Risky patterns or unusual access

Sample policies:
- Restrict access to managed devices only
- Block downloads on personal or unmanaged devices
- Limit access from international or high-risk regions
6. Monitor Security Alerts and Act Swiftly
Prevention isn’t enough. Real-time monitoring and quick response to suspicious activities help minimize damage and maintain operational integrity.
Steps to strengthen monitoring:
- Use Microsoft 365 Security Center for unified monitoring.
- Set automated workflows using Power Automate or Logic Apps.
- Deploy SIEM tools (e.g., Azure Sentinel) for real-time analysis.
- Maintain an incident response plan: define steps, roles, and simulate scenarios.
7. Invest in User Training and Awareness
Human error is a leading cause of data breaches. Educating employees on best practices equips them to become the first line of defense.
Training topics to cover:
- Spotting phishing and suspicious emails.
- Handling confidential files correctly.
- Sharing responsibly with colleagues and guests.
- Reporting potential security issues promptly.
Extras:
- Customize training based on user role.
- Run quarterly phishing simulations to gauge readiness.
8. Control External Sharing and Guest Access
Misconfigured guest access is a major security gap. Properly managing who can share and with whom reduces data leakage and compliance risks.
Best practices:
- Limit sharing to specific domains or trusted users.
- Require sign-in for guests—no anonymous links.
- Set expiration dates on all shared links.
- Monitor external access via reports monthly.
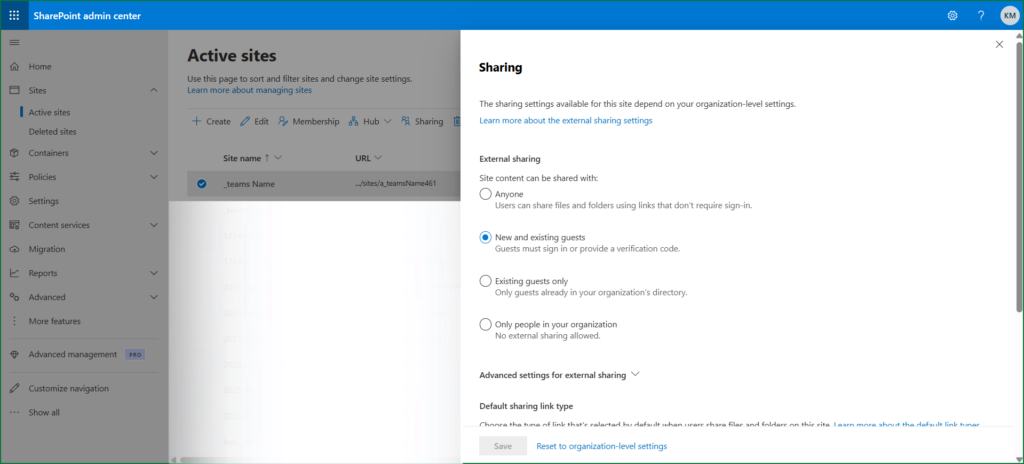
Goal: Strike the right balance between usability and protection.
9. Have a Backup Strategy—Don’t Rely on Recycle Bin
Microsoft’s built-in recovery options are limited in scope and time. Comprehensive backups ensure resilience against data loss from human error, ransomware, or system failures.
Risks without backup:
- Limited retention (30–93 days)
- No full site/library restoration
- No point-in-time recovery for granular content
Recommendation:
- Use enterprise-grade backup tools (e.g., Veeam, Acronis):
- Restore down to single items or full sites
- Retain data long term for compliance
- Cover SharePoint, Teams, and OneDrive holistically
10. Stay Up-to-Date with Security Patches and Updates
Outdated systems are easy targets. Regular patching and staying informed about Microsoft’s latest security features help keep your environment secure.
Even with SharePoint Online, your responsibilities include:
- Updating SPFx solutions, apps, and web parts.
- Ensuring endpoints have the latest OS and browser patches.
- Tracking new features on Microsoft 365 Roadmap.
- Monitoring Message Center announcements.
- Updating hybrid/on-prem components.
Have a patching plan:
- Test patches in a dev environment.
- Roll out in controlled stages.
- Track deployment success and failures.
Common SharePoint Security Mistakes to Avoid
Even the most security-conscious organizations make preventable errors when securing their SharePoint environments. Awareness of these common pitfalls can help you build a more resilient security posture.
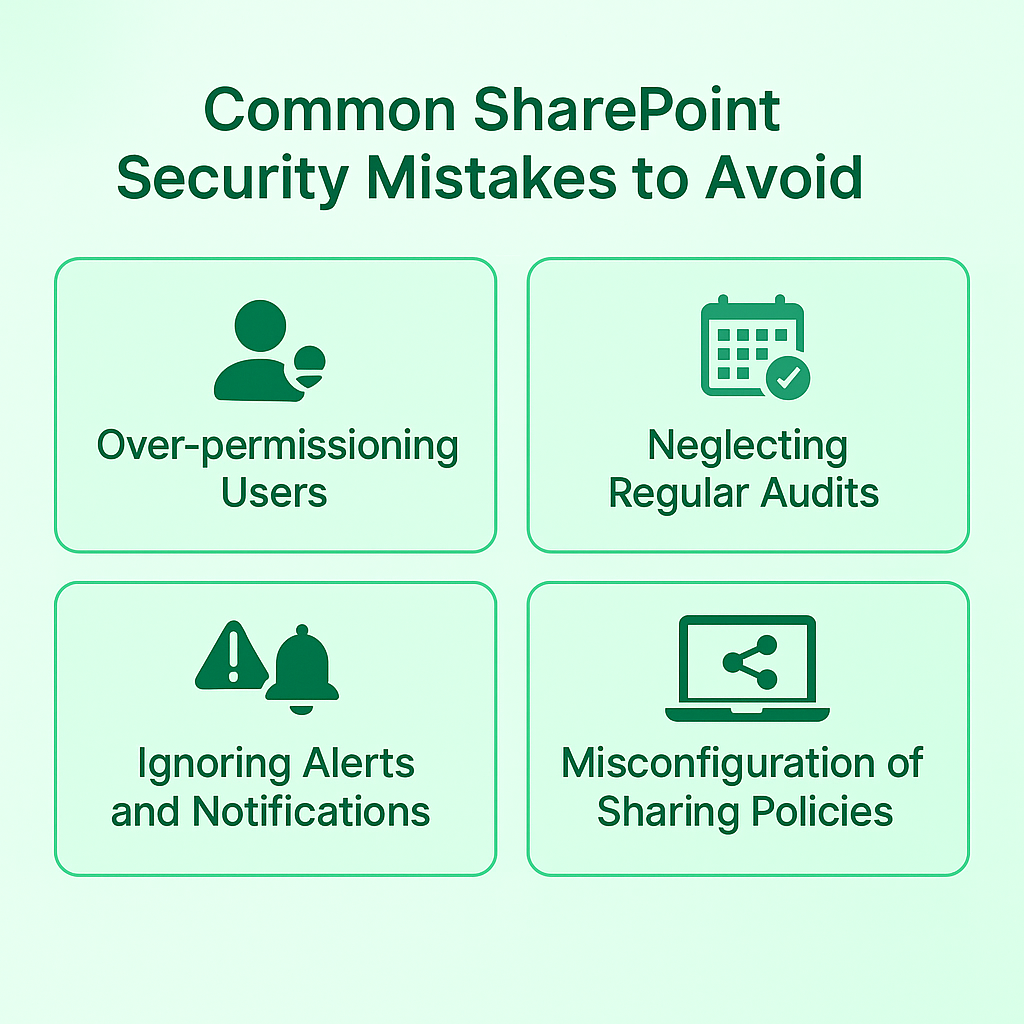
Over-permissioning Users
We’ve all been there – granting higher permissions than necessary just to “make it work.” This convenient shortcut creates serious security risks. The principle of least privilege should guide all access decisions.
Common over-permissioning mistakes include making too many users site collection administrators, using the “Everyone except external users” group excessively, granting “Full Control” when “Contribute” would suffice, and allowing permissions to inherit across unrelated document libraries. Structure your permissions around clearly defined roles with documented access requirements, and regularly review them as responsibilities change.
Neglecting Regular Audits
Many organizations implement strong security controls during initial setup but fail to maintain them over time. Security isn’t a one-time configuration – it’s an ongoing process requiring regular validation.
Establish a consistent audit schedule: monthly reviews of highly privileged accounts quarterly evaluations of general permissions and sharing settings bi-annual comprehensive security assessments, and event-driven audits following organizational changes. Automated auditing tools can reduce the administrative burden while improving consistency and coverage.
Ignoring Alerts and Notifications
Alert fatigue represents a serious security risk. When teams receive dozens of notifications daily critical warnings often get overlooked amid the noise, leaving your environment vulnerable even when warning signs are present.
Fine-tune your alert thresholds to reduce false positives implement alert categorization and prioritization, establish clear escalation paths for different alert types and document response procedures for common scenarios. For larger environments, consider implementing a security orchestration and automated response (SOAR) solution.
Misconfiguration of Sharing Policies
SharePoint’s powerful sharing capabilities often become its greatest security vulnerability when improperly configured. Common mistakes include allowing “Anyone” links by default, not setting appropriate link expiration periods failing to restrict file download capabilities and maintaining inconsistent sharing settings across site collections.
Set default sharing links to “Specific people” limit external sharing to authenticated users where possible enable link expiration for all sharing types apply file download restrictions for sensitive content and regularly review externally shared content.
Table of Contents
Talk to our Microsoft Expert Consultant
Conclusion
Choosing between SharePoint Online and On‑Premise isn’t about one being universally better. It’s about aligning your collaboration platform with how you work, what you must comply with, the resources you have and where you want to invest. The cloud offers agility, continuous improvements and tight integration with modern tools. On‑premise provides control and customisation for specialised or regulated scenarios. Hybrid models let you blend both.
Whatever path you choose, remember that SharePoint’s power goes beyond storage and portals. It’s a foundation for intranets, document management systems and custom apps that streamline operations and reduce manual work. When implemented thoughtfully and paired with the broader Microsoft 365 ecosystem, it becomes a catalyst for digital transformation without the hidden costs of separate software licences.
Share this article

About the Author
Chandru is a technology professional experienced in business automation, Microsoft solutions, and digital transformation. Through practical insights, [he/she/they] helps businesses understand emerging technologies and achieve meaningful outcomes.
Frequently Asked Questions
SharePoint offers strong security, but it’s only as secure as how you set it up! It combines infrastructure protection, data controls, and access management to keep your content safe. The key is properly configuring security features like MFA and permissions—if you neglect these, even Microsoft’s robust protections won’t save you.
Your biggest SharePoint risks come from common mistakes we all make: giving users too many permissions, not checking who has access regularly, ignoring security alerts because there are too many, and setting up sharing links incorrectly. Without proper attention, your sensitive data could be exposed through these everyday oversights.
SharePoint protects your data at three key levels: Infrastructure Security (the physical and technical foundations), Data Protection (keeping content secure through features like DLP), and User Access Control (determining who sees what). User permissions follow a hierarchy from Site Collection Administrators down to simple Viewers, letting you match access to job responsibilities.